
Cybersecurity Radar — 2026-09-26
Attackers exploited a newly disclosed WordPress vulnerability within hours of publication, while security researchers flagged critical SolarWinds flaws and compromised Python packages as fresh RCE and credential-theft risks. ENISA's latest report warns that Europe's technology backbone is increasingly under fire from DDoS, ransomware, and supply chain attacks. With October's Cybersecurity Awareness Month approaching, experts argue traditional security awareness is no longer sufficient against today's threat speed.
Cybersecurity Radar — 2026-09-26
🔴 Critical Alerts
WordPress CVE-2026-87902 exploited within hours of disclosure. Attackers are actively exploiting this WordPress vulnerability to include pearcmd.php and write malicious PHP files when specific theme and server conditions are met. WordPress site administrators should verify their installations are patched and audit for unexpected PHP files.
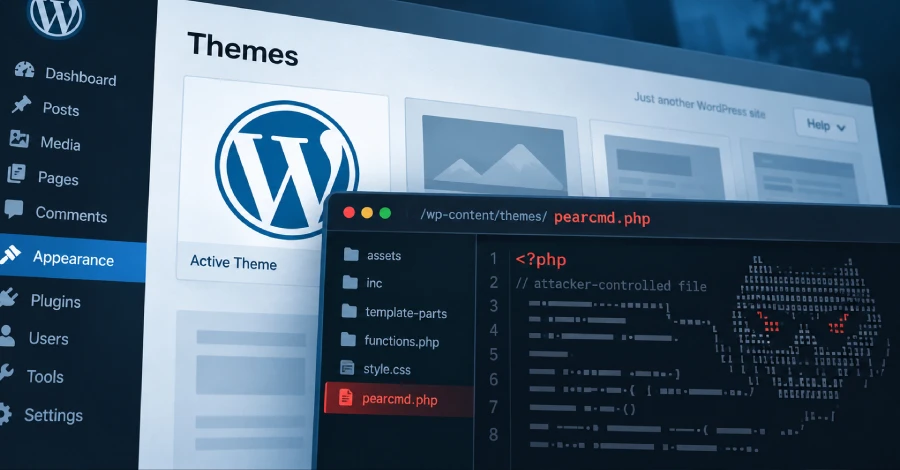
SolarWinds flaws and compromised MemTensor packages create attack opportunities. The September 24 cyber briefing highlights critical SolarWinds vulnerabilities and compromised MemTensor Python packages that enable remote code execution and credential theft — organizations using either should prioritize remediation and dependency auditing.
Threat Landscape
ENISA warns Europe's tech backbone is becoming a cyber target. According to the agency's latest threat report (published September 24), EU companies face sustained pressure from DDoS attacks, ransomware, supply chain breaches, phishing, and growing misuse of AI systems.
Three threat trends defined summer 2026. Dark Reading's latest Reporters' Notebook highlights AI agents breaching Hugging Face, Fairlife's ransomware attack, and threat actors targeting a dozen water systems — a mix of AI-supply-chain compromise, commodity ransomware, and critical infrastructure attacks.

Vulnerabilities & Patches
No verifiably fresh vulnerability or patch data published after 2026-09-24 is available beyond the items covered in Critical Alerts above. Readers should check vendor advisories directly for the latest updates.
Breaches & Incidents
AI-agent compromise adds to 2026 breach tally. The September 24 cyber briefing references an AI-agent breach alongside the SolarWinds and MemTensor package issues, underscoring that AI tooling and software supply chains are now routine breach vectors.
No additional confirmed breach disclosures from the past 24 hours were found in available sources. Note: screenshot-based extraction of the CISA advisories page was incomplete — verify current CISA bulletins directly at cisa.gov.
Industry & Policy
Cybersecurity Awareness Month 2026 marks a strategic turning point. Commentary published this week argues traditional awareness training is no longer sufficient against rapidly evolving threats, framing this October's campaign as a shift toward more risk-based, behavior-focused security programs.
What to Watch
- Exploitation speed: the hours-fast weaponization of CVE-2026-87902 suggests disclosure-to-exploit windows will keep shrinking; patch SLAs must shrink with them.
- AI supply chain risk: the Hugging Face AI-agent breach and compromised MemTensor packages signal a wave of AI-tooling attacks heading into Q4.
- Critical infrastructure: repeated targeting of water systems and October's Awareness Month emphasis on the "3 Rs" for critical infrastructure point to sustained OT focus from both criminals and state actors.
Reader Action Items
- Audit WordPress installations immediately for CVE-2026-87902 indicators: look for
pearcmd.phpinclusion attempts and unexpected PHP files in theme directories. - Review your Python dependency chain for MemTensor packages and your SolarWinds deployments for pending critical updates.
- Take one concrete step before October 1: map which of your systems qualify as critical infrastructure or supply-chain touchpoints and confirm they have MFA and tested backups.
This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
