
Cybersecurity Radar — 2026-10-24
The cybersecurity landscape is currently defined by the urgent aftermath of the "PHP2Shell" disclosure, where attackers began exploiting critical PHP remote code execution flaws four days before public disclosure. Simultaneously, a massive campaign has breached enterprise firewalls exposing over 70,000 credentials, while GitLab issued emergency patches for a maximum-severity RCE vulnerability. Prediction markets are now reflecting heightened anxiety, with traders assigning 58% odds that the worst cyber day of 2026 has yet to occur.
Cybersecurity Radar — 2026-10-24
🔴 Critical Alerts
PHP2Shell Exploitation Pre-Disclosure Amazon Threat Intelligence has confirmed that exploitation attempts for the critical PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619) were observed in MadPot telemetry on October 17, 2026—four days prior to the official public disclosure on October 21. The flaws, rated CVSS 9.2, allow unauthenticated remote code execution.
GitLab Maximum-Severity RCE GitLab has released emergency security updates to address a critical remote code execution vulnerability with a CVSS score of 10.0. This flaw allows unauthenticated attackers to execute arbitrary code on affected servers, necessitating immediate patching for all GitLab instances.
Arista VeloCloud Zero-Day Attackers are actively exploiting an unpatched SQL injection zero-day in Arista's VeloCloud Orchestrator (VCO), the central management system for SD-WAN networks. The advisory was released on October 22, urging immediate mitigation.
Threat Landscape
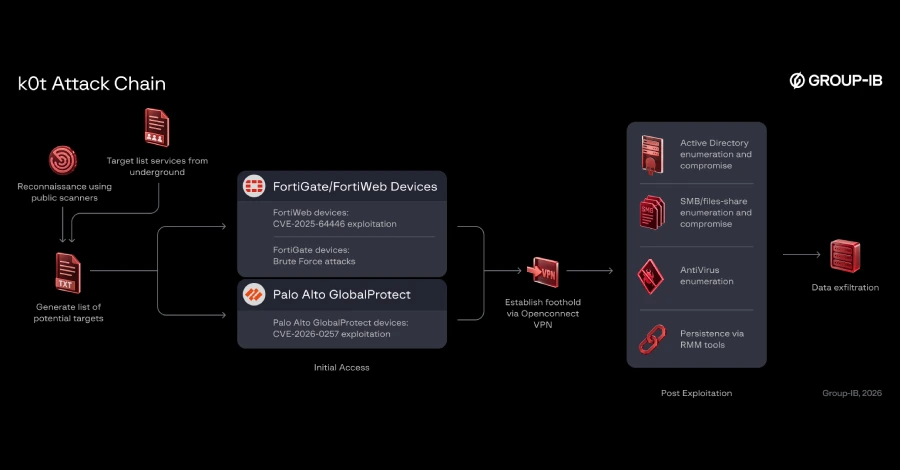
Enterprise Firewall Breach Campaign A campaign attributed to the threat actor "k0t" has successfully breached enterprise firewalls and VPNs, exposing over 70,000 credentials. The attackers utilize Rclone to exfiltrate data and establish persistent access within compromised networks.
Black October Cyberattacks The month of October has been characterized by a shift from awareness to emergency response, with a succession of major attacks casting a shadow over Cybersecurity Awareness Month. Organizations are facing an elevated threat environment requiring immediate defensive postures.
AI-Driven Threats Recent reports from ENISA, Verizon, and Microsoft indicate that AI-assisted attacks, phishing, and ransomware remain the top enterprise cybersecurity risks for 2026, with AI increasingly weaponized to accelerate attack speeds and sophistication.
Vulnerabilities & Patches
PHP Emergency Patches PHP has released emergency updates to address CVE-2026-109618 and CVE-2026-109619, both critical unauthenticated RCE flaws rated CVSS 9.2. Administrators are urged to upgrade to patched releases immediately or apply vendor backports if on older versions.
GitLab Regex Compiler Flaw In addition to the maximum-severity RCE, GitLab patched a critical Regular Expression Compiler flaw that could allow remote attackers to run arbitrary code. This update is part of a broader emergency security release.
Microsoft AI Phishing Detection Microsoft has announced plans to add AI-powered phishing detection to Teams messages starting in early November 2026, aiming to combat the rising tide of social engineering attacks.
Breaches & Incidents
70,000+ Credentials Exposed The breach of enterprise firewalls and VPNs by "k0t" has resulted in the exposure of over 70,000 credentials. This incident highlights the critical risk posed by unpatched network edge devices and the ease with which attackers can pivot from initial access to data exfiltration.
Healthcare Data Breach Statistics New statistics released by HIPAA Journal highlight the ongoing scale of healthcare data breaches in the United States, with 2026 figures showing continued high volumes of incidents and HIPAA violations.
Industry & Policy
Prediction Market Anxiety Traders on Manifold Markets have assigned 58% odds that the "worst day in cyber security in 2026" is still ahead, reflecting a pervasive sense of vulnerability and anticipation of a major catastrophic event.
INTERPOL Law Enforcement Action INTERPOL announced a coordinated law enforcement action that disrupted 10,909 malicious networks and recovered more than $105 million in illicit funds, alongside arrests by agencies from 21 countries.
What to Watch
- Post-Patch Exploitation: Monitor for continued exploitation attempts against PHP and GitLab servers that fail to apply the emergency patches released in late October.
- AI-Augmented Phishing: Keep an eye on the rollout of Microsoft's AI phishing detection in Teams, which may signal a shift in how enterprise platforms handle social engineering.
- Edge Device Security: The "k0t" campaign underscores the need to monitor unpatched firewalls and VPNs, which remain prime targets for initial access brokers.
Reader Action Items
- Patch PHP and GitLab Immediately: If you operate PHP servers or GitLab instances, apply the latest emergency security updates immediately to mitigate CVSS 9.2 and 10.0 vulnerabilities.
- Audit Edge Devices: Review your enterprise firewalls and VPNs for signs of compromise or unpatched firmware, specifically looking for indicators related to the "k0t" campaign.
- Review Teams Security Settings: Prepare for the November rollout of AI-powered phishing detection in Microsoft Teams by reviewing your current phishing policies and user training.
This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
