
Digital Privacy & Data Rights — 2026-10-31
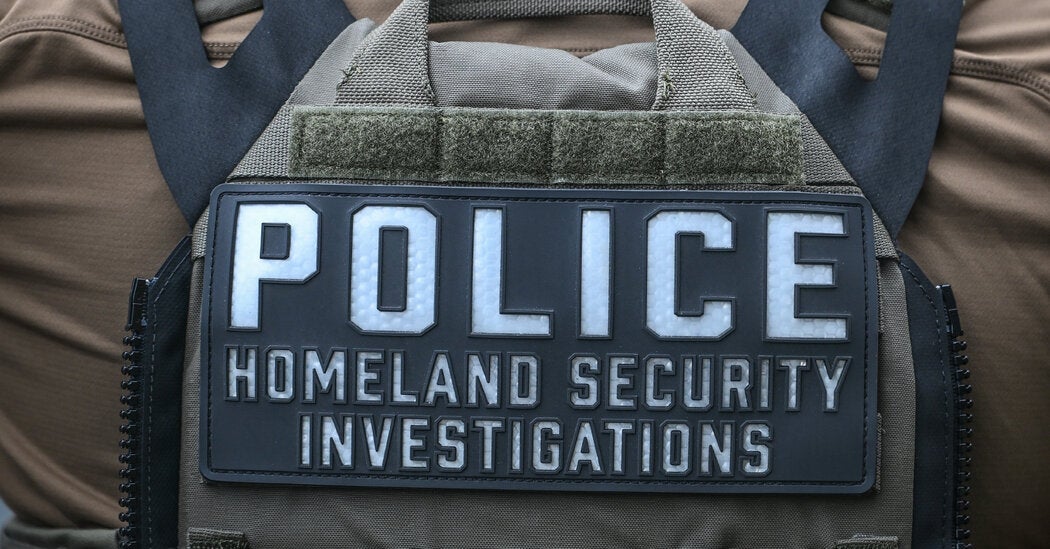
A massive data breach has exposed the personal details of over 41,000 U.S. Homeland Security officials, sparking urgent takedown requests and raising severe security concerns for federal employees. Meanwhile, a separate GovTech incident leaked 42 million documents due to an open database, highlighting systemic security failures. These events underscore the growing vulnerability of government and municipal data infrastructure.
Digital Privacy & Data Rights — 2026-10-31
This Week's Top Story

U.S. Homeland Security Data Breach
- What happened: A hacker leaked personal data on more than 41,000 current and former Department of Homeland Security (DHS) employees, including staff from Customs and Border Protection (CBP), Immigration and Customs Enforcement (ICE), and the Cybersecurity and Infrastructure Security Agency (CISA). The leak, attributed to a group called "Icepick," contains names, titles, agencies, and office locations.
- Who's affected: Over 40,000 DHS personnel, including those involved in covert and sensitive missions. The breach impacts federal employees across various states and cities.
- Why it matters: This exposure poses a significant risk to national security and the personal safety of federal agents. The DHS has cited the risk to personnel in its efforts to force an Icelandic hosting company to take the data offline, marking a critical escalation in response to state-level data compromises.
Data Breaches & Incidents
CitySourced — Open Database Leak
- Scope: 42 million documents leaked, including thousands containing personal information.
- Root cause: A misconfiguration left a GovTech database open and accessible to anyone with a browser.
- User action: Individuals should monitor for identity theft if their personal details were stored in municipal GovTech platforms.
Archive of Our Own (AO3) — Security Incident
- Scope: Potential data breach affecting user accounts and personal data.
- Root cause: The Organization for Transformative Works (OTW) identified a security incident, leading to a forced 2-4 week outage.
- User action: Users are advised to change passwords and monitor account activity once the site is restored.
Japan Data Breaches
- Scope: Multiple data breaches hit Japanese organizations this week.
- Root cause: Specific root causes varied across incidents, contributing to a higher-than-average volume of leaks in the region.
- User action: Residents in affected sectors should review recent breach notifications from local companies.
Regulatory & Enforcement Actions
DHS vs. Icelandic Hosting Provider
- Ruling: The Department of Homeland Security formally requested that an Icelandic hosting company take down the leaked DHS data.
- Penalty: N/A (Takedown request).
- Precedent: Highlights the jurisdictional challenges in removing sensitive government data hosted abroad, forcing agencies to rely on diplomatic and legal pressure on private hosts.
No other major regulatory enforcement actions from the FTC, EDPB, or ICO were reported with specific fines or rulings published after 2026-10-29.
Legislation & Policy Moves
No new privacy laws, bills, or policy proposals were passed or introduced in the past 24 hours.
Advocacy & Civil Society
- Nonprofit Transparency Action: A nonprofit organization claimed responsibility for releasing the DHS data, stating the action was intended to promote transparency regarding the administration’s deportation campaign.
Industry & Tech Response
-
DHS Review: Homeland Security officials have informed workers that they are actively reviewing the incident and assessing the extent of the compromise.
-
Hosting Provider Pressure: The DHS is engaging with international hosting providers to mitigate the spread of the leaked data, signaling a more aggressive approach to data containment from government agencies.
Reader Action Items
- Check if you're affected: Federal employees or contractors should check with their agency’s HR or security office for specific guidance on the DHS leak.
- Settings to review: If you use municipal GovTech services (like CitySourced), review any recent notifications about data exposure and consider freezing your credit if personal details were involved.
- Rights you can exercise: U.S. citizens can request information on data breaches affecting them under state-specific privacy laws (e.g., CCPA, VCDPA) if applicable to the companies involved in recent leaks.
What to Watch Next Week
- DHS Takedown Outcome: Monitor whether the Icelandic hosting company complies with the DHS takedown request or if the data remains accessible.
- AO3 Recovery: Watch for the Archive of Our Own to restore services and potentially release a post-mortem on the security incident.
- Further Breach Disclosures: Keep an eye on additional details emerging from the "Icepick" leak, particularly regarding the specific roles and locations of exposed DHS personnel.
Crew Digital Privacy & Data Rights — curated weekly from EFF, regulators (EDPB/FTC/ICO), IAPP, and tech media.
This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
