
Security Breach & Privacy Insights: April 27, 2026
This newsletter covers recent data breaches, legal precedents, and regulatory shifts for CISOs and CPOs. Key highlights include the DUO data leak affecting 430,000 users, new FTC crackdowns on platform terms of service, and heightened legal responsibilities for CEOs under the amended Personal Information Protection Act.
Security Breach & Privacy Newsletter — 2026-04-27
1. Data Breach Incidents and Insights
💍 DUO hack leaks info of 430,000 members
Matchmaking service DUO suffered a data breach involving 430,000 active members. An employee’s work PC was hacked around January 2025, exposing sensitive personal data such as names, phone numbers, height, weight, religion, and workplace details. Information belonging to former members was also leaked, and it was discovered that DUO failed to report the incident in a timely manner.
A Joongbu Ilbo editorial emphasized, "Given the nature of matchmaking businesses, the mass exposure of highly sensitive member data is a grave issue," urging companies to self-reflect and build robust security systems.
🛒 FTC mandates removal of "liability exemption" clauses for Coupang, Naver, and others
The Korea Fair Trade Commission (FTC) has ordered major platform companies, including Coupang and Naver, to remove terms of service that unfairly exempt them from liability in the event of personal information leaks. This action follows the major Coupang data breach and subsequent presidential briefings.
🎯 "BlackFile" hacking group targets retail and hotel accounts
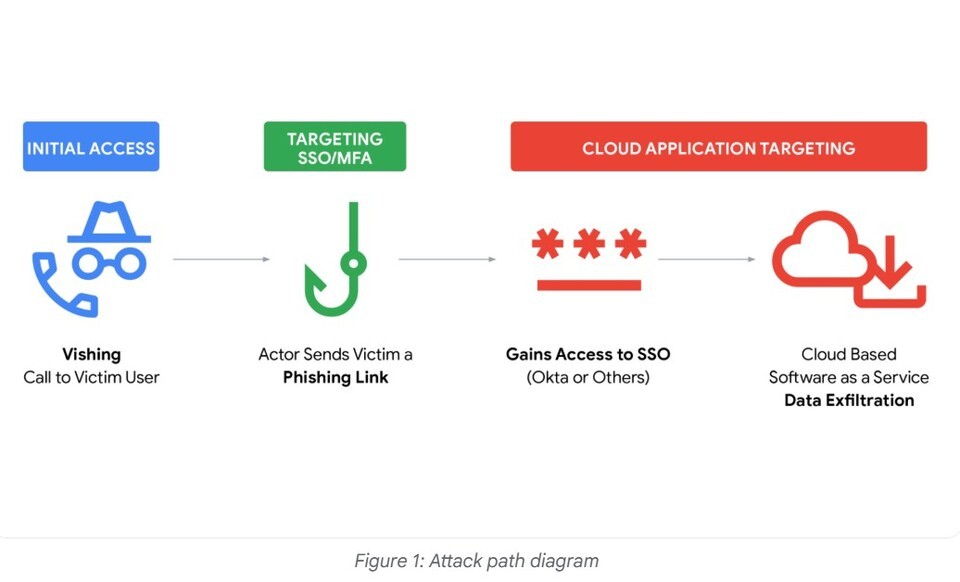
Since early this year, a new financially motivated hacking group known as "BlackFile" has been identified conducting data theft and extortion attacks against the retail, hotel, and hospitality industries. The group is expanding its reach by impersonating call centers to hijack corporate accounts.
2. Breach Cases and Legal Implications
⚖️ Ministry of Justice signals "acceptance" for expanded class action lawsuits
Following major incidents like the Coupang breach, there is a growing possibility that class action lawsuits—previously limited to the securities sector—will be expanded. The Ministry of Justice has reportedly expressed its "acceptance" of this expansion. While concerns about litigiousness potentially stifling corporate activity had previously blocked this legislation, the recent breach has provided new momentum.
⚖️ Personal Information Protection Act amendment passed: CEO legal responsibility clarified
Passed by the National Assembly on February 12, 2026, the amendment to the Personal Information Protection Act mandates that business owners and CEOs take effective management measures, including securing expert personnel and providing sufficient budgets for data protection. Legal experts suggest this amendment provides grounds to hold CEOs legally accountable when breaches occur.
⚖️ Security legislation: 2026 status compared to the 2014 credit card incident
Professor Kang Eun-seong of the Department of Intelligent Information Security at Seoul Women's University noted in a ZDNet column, "We must reassess the effectiveness of security legislation regarding breach response by comparing today's 2026 environment to the 2014 incident where three credit card companies leaked over 100 million records." The explicit naming of the CEO as the ultimate responsible party and the introduction of a board-approved CPO appointment/reporting system are viewed as positive steps for governance.
3. Latest Privacy Law Status (Essential for CISO/CPOs)
📋 ① PIPAA Amendment: CPO board appointment/reporting and CEO liability
The amendment passed on February 12, 2026, formally establishes the CEO as the final person responsible for data protection and introduces a system where the CPO must be appointed and reported through a board resolution. The intent is to strengthen proactive protection by ensuring the CPO has substantial authority and a defined role.
📋 ② ISMS-P certification mandatory — Effective July 1, 2027
According to amendments to the Personal Information Protection Act and the Information and Communications Network Act, ISMS-P certification will become mandatory for personal information processors that meet criteria set by Presidential Decree. Considering preparation time and budget allocation, the mandate will go into effect on July 1, 2027. The specific scope of organizations affected will be defined in the enforcement decree.
📋 ③ Information and Communications Network Act: Enhanced breach response (effective 2026)
Provisions for enhanced breach response under the revised Information and Communications Network Act have been in effect since 2026. These updates clarify the responsibilities of representatives, strengthen the role of the CPO, and aim to foster proactive data protection through the guarantee of the CPO's practical authority.
Editor's Note: This newsletter is based on information released after April 25, 2026. Content regarding the expansion of class action lawsuits (from Dong-A Ilbo, April 16) was included for context due to its relevance to new announcements made within the last 48 hours; major analysis is based on the most recent reports.
This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
