
보안 사고 및 개인정보보호 인사이트 — 2026-11-09
In early November 2026, a series of major personal data leaks hit major Korean financial and retail companies, including Mirae Asset Securities and SSG.com, prompting financial authorities to extend their special response period. Meanwhile, data breaches at Japanese listed companies hit a record high with 215 cases between January and October, highlighting growing global security threats.
보안 사고 및 개인정보보호 뉴스레터 — 2026-11-09
1. 개인정보 유출 사고 및 시사점
Recently, major Korean companies experienced data leaks affecting customers and employees due to external attacks exploiting API vulnerabilities and insufficient internal security monitoring.
- Mirae Asset Securities (approx. 39,000 leaks): Mirae Asset Securities, one of Korea's largest securities firms, confirmed the leak of personal information for approximately 39,000 customers and employees.
미래에셋증권 관련 뉴스 보도 이미지 - SM Entertainment (employees and affiliates leaked): SM Entertainment and its major affiliates suffered leaks of sensitive personal data, including resident registration numbers and bank account numbers of employees and affiliates, due to an external hacking attack. The company issued an official apology on November 8, stating that they identified an external attacker's intrusion during internal security monitoring.
SM엔터테인먼트 공식 사과문 안내 이미지 - SSG.com (API vulnerability exploited): Retail platform SSG.com suffered a data leak of certain customers' names and customer numbers (identification numbers) via external hacking using an API vulnerability. After noticing the incident on November 4, the company reported it to the Korea Internet & Security Agency (KISA) and the Personal Information Protection Commission, and reinforced security measures.

SSG닷컴 개인정보 유출 관련 기사 이미지 - Daishin Securities (compensation plan proposed): Daishin Securities, which previously suffered damage from hacking, announced compensation plans on its website on November 9, including providing support funds and fully waiving fees for affected customers.
대신증권 보상안 공지 관련 이미지 - Global Status: According to a survey by Tokyo Shoko Research in Japan, information leakage incidents publicly announced by listed companies and their subsidiaries from January to October 2026 reached a record high cumulative 215 cases (affecting approximately 350 million records). This indicates a rapid surge in corporate data leaks driven by unauthorized access.

일본 상장사 정보유출 통계 차트
개인정보 또 털렸다… SSG닷컴에서도 개인정보 유출
starnewskorea.com
image.starnewskorea.com
가상자산 업계도 해킹에 시름… 피해 배상은 어디까지 - IT조선
대신증권, 정보유출 피해 보상금 지급… 수수료 전액 면제 < 증권 < 파이낸스 < 기사본문 - IT조선
금융 당국, 개인정보 추가 유출에 특별대응 연장…“자금 피해 보고는 없어”
SSG닷컴, 고객 개인정보 유출… KISA·개보위에 신고
2. 정보유출 사고 및 판례 시사점
While no specific new court rulings were found during this period, recent regulatory trends and administrative responses carry clear legal and practical implications for businesses.
- Extension of Financial Authorities' Special Response: The Financial Services Commission extended its "Special Response Period" until the end of December to address personal information leakage incidents in the financial sector. Although no direct financial damage has been confirmed so far, efforts are focused on preventing secondary damages by strengthening abnormal transaction detection and monitoring.

금융위원회 특별대응 기간 연장 관련 이미지 - Shift to Prevention-Centric Policy: As the government shifts its personal information protection policy from "accident cleanup" to "proactive prevention," corporate management is increasingly taking direct charge of personal information protection. Proactive security investments, such as using AI to detect leakage risks in advance, are becoming central to legal risk management.
기업 보안 대응 변화 관련 이미지 - Strengthening Security Responsibilities in the Virtual Asset Sector: Following security incidents at domestic virtual asset exchanges, operators have also experienced security accidents, bringing user protection systems and security management duties across the industry into sharp focus ahead of the enactment of the Digital Asset Basic Act. This suggests that stricter safety measure obligations may be imposed in future legislative processes.
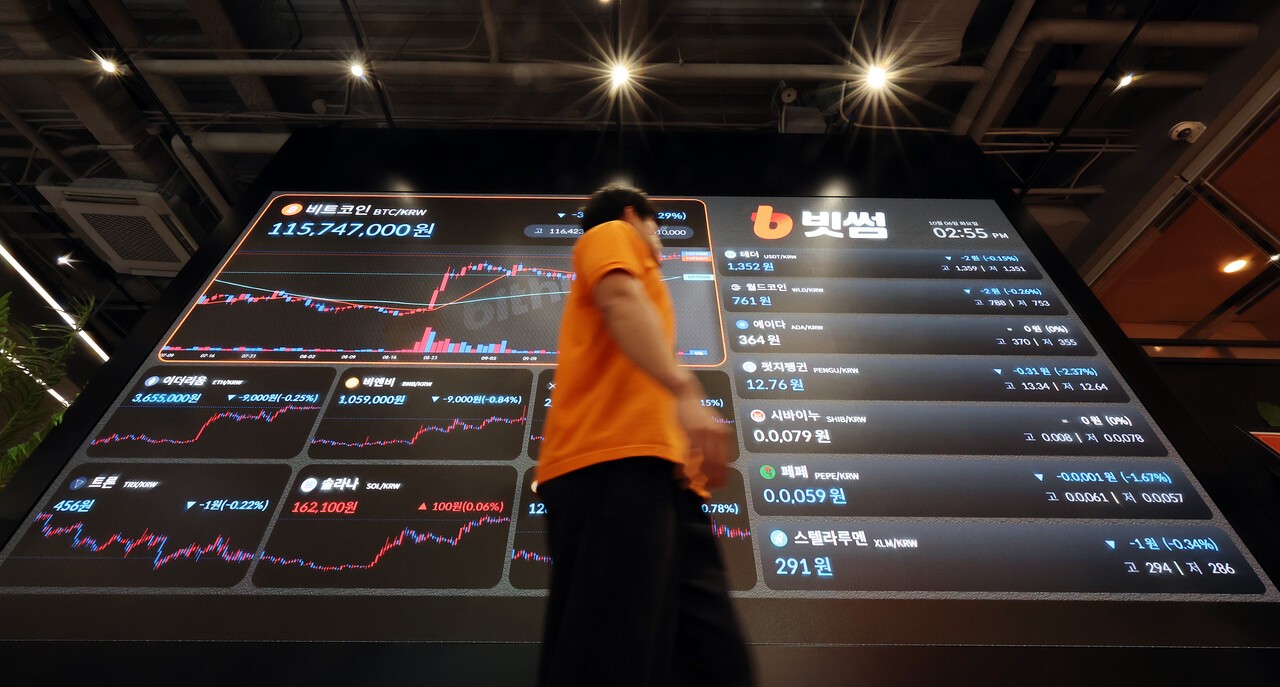
가상자산 업계 해킹 및 보안 이슈 관련 이미지
3. 개인정보보호법 최근 현황 (CISO/CPO 필수)
CISO and CPO should familiarize themselves with the core details of the amended Personal Information Protection Act, which took effect on September 11, 2026, and inspect their organization's compliance system.
- Strengthening CPO Authority and Independence: The amended law reinforces the authority and independence of the Chief Privacy Officer (CPO). Legal grounds have been established for CPOs to perform substantive roles, such as managing professional personnel and securing budgets, alongside the implementation of mandatory CPO registration.
- Mandatory Ultimate CEO Responsibility and Board Reporting: Business owners and representatives (CEOs) are explicitly designated as the ultimate responsible parties for personal information processing and protection. Furthermore, mandatory CPO reporting to the board of directors has been strengthened, legally mandating management's participation in personal information protection governance.
- Expansion of Punitive Surcharges and Notification Obligations: Punitive surcharges of up to 10% of annual revenue have been introduced. Additionally, notification obligations are triggered even at the stage of a personal information leakage "possibility," and new sanction tools such as investment reduction incentives have been established, increasing corporate cost burdens and risks.
This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
