
보안 사고 및 개인정보보호 뉴스레터 (2026-09-21)
This newsletter covers recent security breach incidents, relevant legal precedents, and regulatory changes for CISO/CPO. IMPORTANT: ONLY report claims explicitly stated in your sources. Do not supplement with prior knowledge or assumptions.
보안 사고 및 개인정보보호 뉴스레터 — 2026-09-21
This newsletter covers recent security breach incidents, relevant legal precedents, and regulatory changes for CISO/CPO. IMPORTANT: ONLY report claims explicitly stated in your sources. Do not supplement with prior knowledge or assumptions.
1. 개인정보 유출 사고 및 시사점
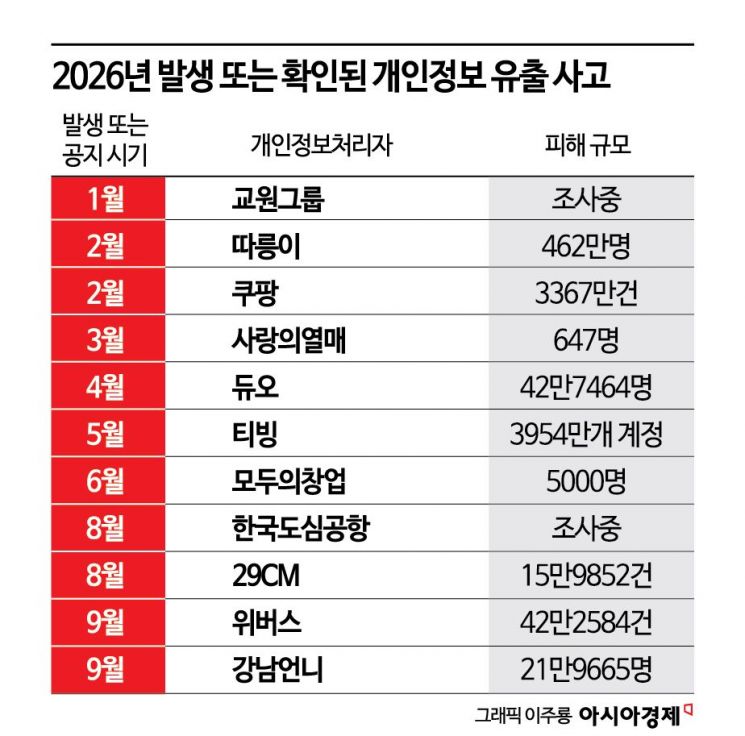
Here is a roundup of recent major personal data breach incidents.
- 카카오게임즈: Around September 14, 2026, external hacking targeting Kakao Games' 'Partners' and 'RINK' services resulted in the leakage of personal information for 140 users. The company immediately blocked the system pathways, reported the incident to relevant authorities, and is currently investigating the exact cause and scope of the impact through a specialized security agency.
- 한국지역정보개발원(KLID): On September 14, 2026, a personal data leak was confirmed in the webmail system of the Korea Local Information Development (KLID). The scale of the leak remains private.
- 레벨13 (룩핀): Level 13, which operates the men's fashion platform 'Lookpin', suffered a customer data breach involving emails and passwords. The breach was found to be caused by external access exploiting security vulnerabilities in the data analysis tool 'Metabase'.

2. 정보유출 사고 및 판례 시사점
Here are recent security-related court rulings and their legal implications for businesses.
- 대법원, 정신적 손해 없는 개인정보 유출에 대한 기업 배상 면책 판결: The 1st and 2nd instance courts acknowledged company negligence regarding the failure to detect and block hacking attacks—such as disabling the web firewall. However, the Supreme Court ruled to exempt the company from liability for damages, considering factors including: ▲ the existence of pre-encrypted passwords ▲ the difficulty in concluding that data subjects were exposed to specific risks based solely on leaked email addresses ▲ the lack of evidence that the hacked information was transferred or spread to third parties ▲ and the fact that the company reported the incident to the Personal Information Protection Commission immediately. This suggests that a company's post-incident response and implementation of technical protection measures become core factors in determining legal liability when a breach occurs.
- AI 발전에 따른 보안 취약점 및 법적 책임 논의: Recent articles pointed out that the rapid advancement of AI technologies makes it easier to exploit security vulnerabilities that were previously hard to discover, while defense capabilities have not been sufficiently upgraded. While past courts had difficulty holding companies generally negligent for lax safety measures during large-scale customer data leaks, analyses suggest that the scope of corporate liability may be re-evaluated alongside the rise of AI-driven attacks.
3. 개인정보보호법 최근 현황 (CISO/CPO 필수)
Here are recent legal amendments and regulatory compliance statuses that CISOs and CPOs must be familiar with.
- 개정 「개인정보 보호법」 시행 (2026년 9월 11일): The amended Personal Information Protection Act, which had passed the National Assembly plenary session and been promulgated, officially took effect. This amendment includes changes that alter overall corporate management risk and practical processes, such as expanding the legal concept of a breach, a major shift in notification timing, and imposing penalties of up to 10%.
- 최종 책임자 의무 명시: The amended law explicitly specifies overall management duties for the chief executive, including providing expert personnel and budget support necessary for personal information protection. This means that personal information protection governance has been elevated to the executive management and board of directors level.
- CI(연계정보) 유효기간 도입 논의: With successive leaks of Connection Information (CI) due to large-scale data breaches, voices are growing to introduce validity periods for CI and renew them periodically. Reflecting the characteristics of CI—which, unlike passwords or card numbers, is difficult for users to change once leaked—Rep. Cho Kyung-tae raised the argument that it should be renewed every year.

This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
