
보안 사고 및 개인정보보호 인사이트 (2026-11-02)
Hey there! This newsletter breaks down recent major data breaches at companies like HYBE and Hyundai Ezwel, and looks at how they're handling things. We'll also dive into the updated Personal Information Protection Act from September 2026—especially the stricter CISO/CPO rules—and the ongoing challenge of low hacking arrest rates.
보안 사고 및 개인정보보호 뉴스레터 — 2026-11-02
1. 개인정보 유출 사고 및 시사점
Lately, we've seen a wave of massive data leaks hitting major domestic companies here. Super-sensitive info from both the entertainment and retail sectors got exposed, so consumers definitely need to keep their guard up.
1. HYBE: Massive Leak of Partner and Employee Info HYBE, one of the top entertainment giants in the country, suffered a major data breach due to an external cyberattack that came to light later on. The incident exposed a huge chunk of ultra-sensitive data, including resident registration numbers, bank accounts, and medical info for partner agencies as well as current and former staff.
2. Hyundai Ezwel: Customer Data Leak and Compensation Plans Welfare platform provider Hyundai Ezwel also had a security slip-up where customer personal data leaked externally. The company stepped up to say they will fully compensate any verified damages and are actively working to stop secondary scams using the leaked info.
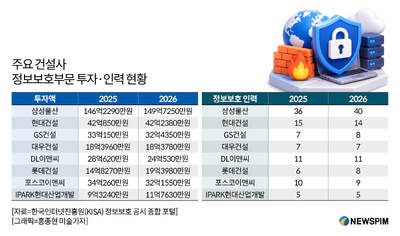
3. GS E&C: Apartment Community Booking System Hacked Over at GS E&C, a resident data leak hit their apartment community reservation system. As construction firms expand digital platforms to offer fancy residential services, there's more than a tenfold security investment gap between them, which is fueling worries about similar accidents down the road.
2. 정보유출 사고 및 판례 시사점
Even with the Personal Information Protection Commission tightening up enforcement rules, it looks like real-world legal action and catching cybercriminals still have a ways to go.
1. Low Hacking Arrest Rates vs. Heavier Fines While penalty criteria for massive data leaks got stricter starting September 11, the arrest rate for hacking and network intrusion crimes remains pretty low. This goes to show that tightening regulations alone won't stop attacks—boosting investigative muscle is an urgent priority.
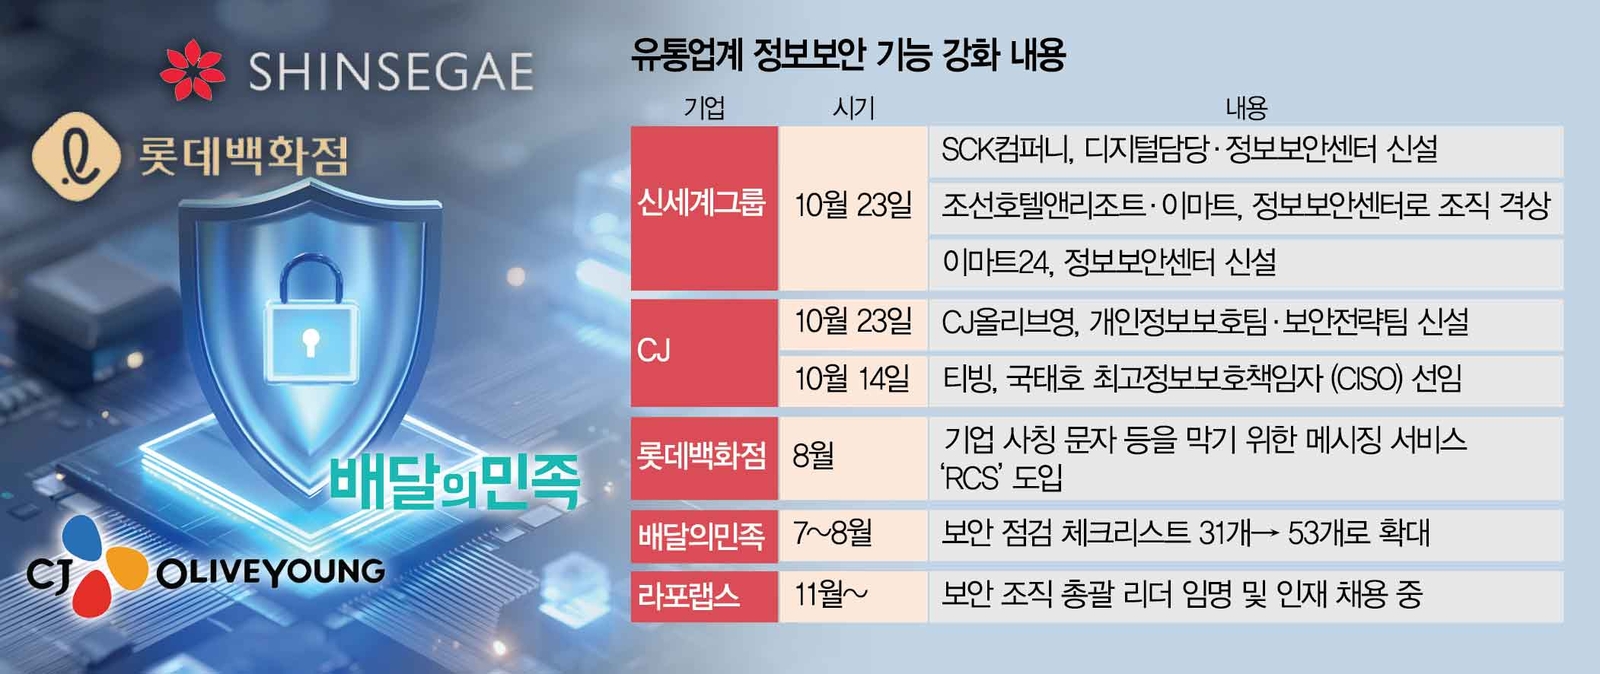
2. Retailers Giving Security Teams a Makeover Following these back-to-back leaks, major retail players like Olive Young (Olive Seven) and Starbucks are beefing up their internal controls by setting up or revamping dedicated information security teams. In a digital world where everyone relies more on customer data, keeping privacy locked down has become a matter of corporate survival.
3. 개인정보보호법 최근 현황 (CISO/CPO 필수)
Chief Information Security Officers (CISOs) and Chief Privacy Officers (CPOs) really need to get up to speed on the revised Personal Information Protection Act that kicked in on September 11, 2026, along with its follow-up rules.
1. Mandatory CPO Registration and Expanded Powers Since September 11, 2026, registering your CPO has become legally required. The updated law gives CPOs more teeth and independence, cementing their role as a legal must-have in a company's privacy management setup.
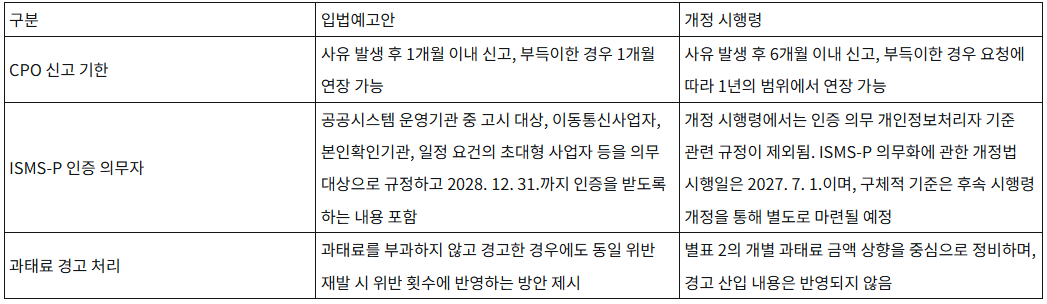
2. Punitive Fines and Mandatory Board Approval The revised law explicitly names business owners and CEOs as the ultimate heads of personal data processing and protection, bringing in punitive fines of up to 10% and an investment reduction incentive system. Plus, requirements for CPOs to manage specialized staff, secure budgets, and report to the board have been beefed up, making board-level votes on security spending totally mandatory.
3. Upcoming ISMS-P Certification Mandates Following the September revisions, amendments to the Network Act and mandatory ISMS-P certifications are rolling out through the first and mid-parts of 2027. Since executive-level CISO appointment rules are shifting, CISOs need to get their systems tuned up ahead of time to snag those certifications.

This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
