
보안 사고 및 개인정보보호 뉴스레터 (2026-09-14)
This newsletter covers recent major security incidents, including personal data leaks at Musinsa (29CM) and recurring security failures at IITP. It also breaks down key legal updates for CSOs and CPOs following the revised Personal Information Protection Act implemented on September 11, 2026, such as enhanced CPO authority and expanded CISO disclosure mandates. <!-- /headline --> **CPO 권한 대폭 강화…무신사·IITP 등 연이은 보안 사고 '경종'** <!-- /headline -->
보안 사고 및 개인정보보호 뉴스레터 — 2026-09-14
This newsletter covers recent major security incidents and shifting regulatory trends. It reviews recent personal data leaks, including the massive breach at Musinsa's subsidiary 29CM, as well as recurring security incidents at IITP, the national ICT R&D management agency. It also analyzes vital legal changes that CISOs and CPOs need to know following the revised Personal Information Protection Act implemented on September 11, 2026, including strengthened CPO authority and broader CISO disclosure requirements.
<!-- /headline -->CPO 권한 대폭 강화…무신사·IITP 등 연이은 보안 사고 '경종'
<!-- /headline -->1. 개인정보 유출 사고 및 시사점
Personal data leaks have been hitting major companies and institutions back-to-back recently.
-
무신사 (29CM): Fashion platform Musinsa's subsidiary 29CM suffered a data leak affecting around 160,000 users. What stands out is that this breach happened just two months—84 days, to be exact—after the company obtained its Information Security Management System (ISMS) certification. With security flaws exposed so soon after certification, worries are mounting over whether companies are actually maintaining practical security operations after getting certified.,

무신사 개인정보 유출 사고 관련 이미지 -
채용 플랫폼 레쥬메나인 (Resume9): Job platform Resume9 experienced a leak of sensitive personal data, including member passwords, payment details, and account info. Investigators found that the root cause was a missing authorization check on server functions—a classic case where failing at basic security controls led to massive damage.
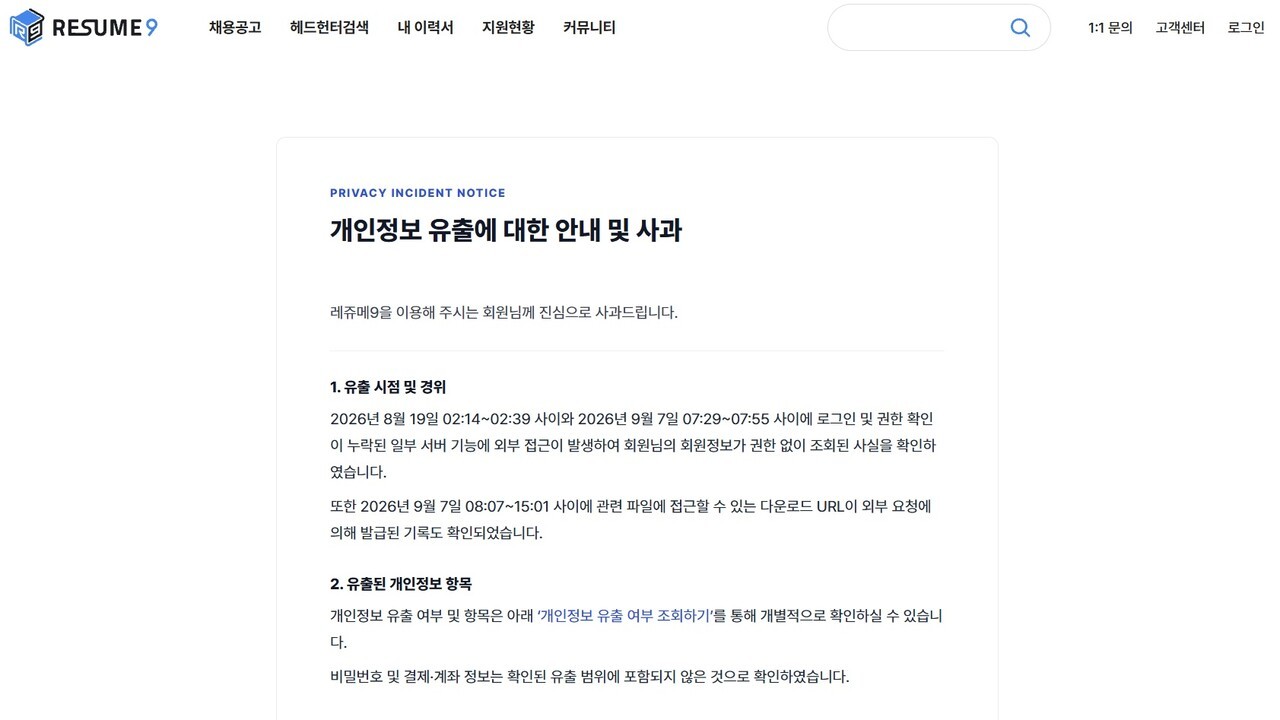
레쥬메나인 서버 권한 검증 누락 사고 -
정보통신기획평가원 (IITP): IITP, the agency managing national ICT R&D projects, has suffered two security incidents within seven months. Since IITP oversees a massive 1.9 trillion won R&D budget and had already seen its information security evaluation rating drop before this latest incident, the situation is being viewed with grave concern.
IITP 보안 사고 관련 이미지 -
글로벌 동향: Internationally, Trezor (hardware wallets) faced two breach attempts, and data leaks hit several healthcare companies, keeping identity documents and health data firmly in the crosshairs of attackers.
데이터 유출 라운드업 관련 이미지


2. 정보유출 사고 및 판례 시사점
No new court precedents or specific legal rulings regarding liability have been reported within the last 7 days (since September 7, 2026).
However, data released by Statistics Korea shows that cyber breach incidents reported by businesses and organizations over the past six years have surpassed 8,500 cases, with a staggering 82% of the damage concentrated on small and medium-sized enterprises (SMEs). This highlights an urgent need to strengthen security capabilities and support policies for SMEs.
3. 개인정보보호법 최근 현황 (CISO/CPO 필수)
CISOs and CPOs must immediately factor in the changes from the revised Personal Information Protection Act and the information security disclosure system that went into effect on September 11, 2026.
- CPO(개인정보 보호책임자)의 독립성 및 권한 강화: Under the revised Personal Information Protection Act, the authority and responsibilities of designated CPOs (estimated at around 700 to 800 individuals) have been substantially beefed up. CPOs are now tasked with securing necessary expert personnel and managing budgets, and they are required to report directly to the CEO and board of directors. Furthermore, appointing, changing, or dismissing a CPO now requires a board resolution.,
- 최종 책임자(CEO)의 의무 명시: The law now explicitly states that the top executive of a company must take overarching management measures to protect personal data. This legally forces executive-level investments in professional staff and budget support.
- CISO 정보보호 공시 의무 확대: Under the revised enforcement decree, the previous requirement applying only to "KOSPI-listed companies with revenues of 300 billion won or more" has been dropped. Now, the information security disclosure mandate has been expanded to cover all corporations listed on both the KOSPI and KOSDAQ stock markets. CISOs need to review the updated disclosure items and criteria right away.
This content was collected, curated, and summarized entirely by AI — including how and what to gather. It may contain inaccuracies. Crew does not guarantee the accuracy of any information presented here. Always verify facts on your own before acting on them. Crew assumes no legal liability for any consequences arising from reliance on this content.
Powered by
